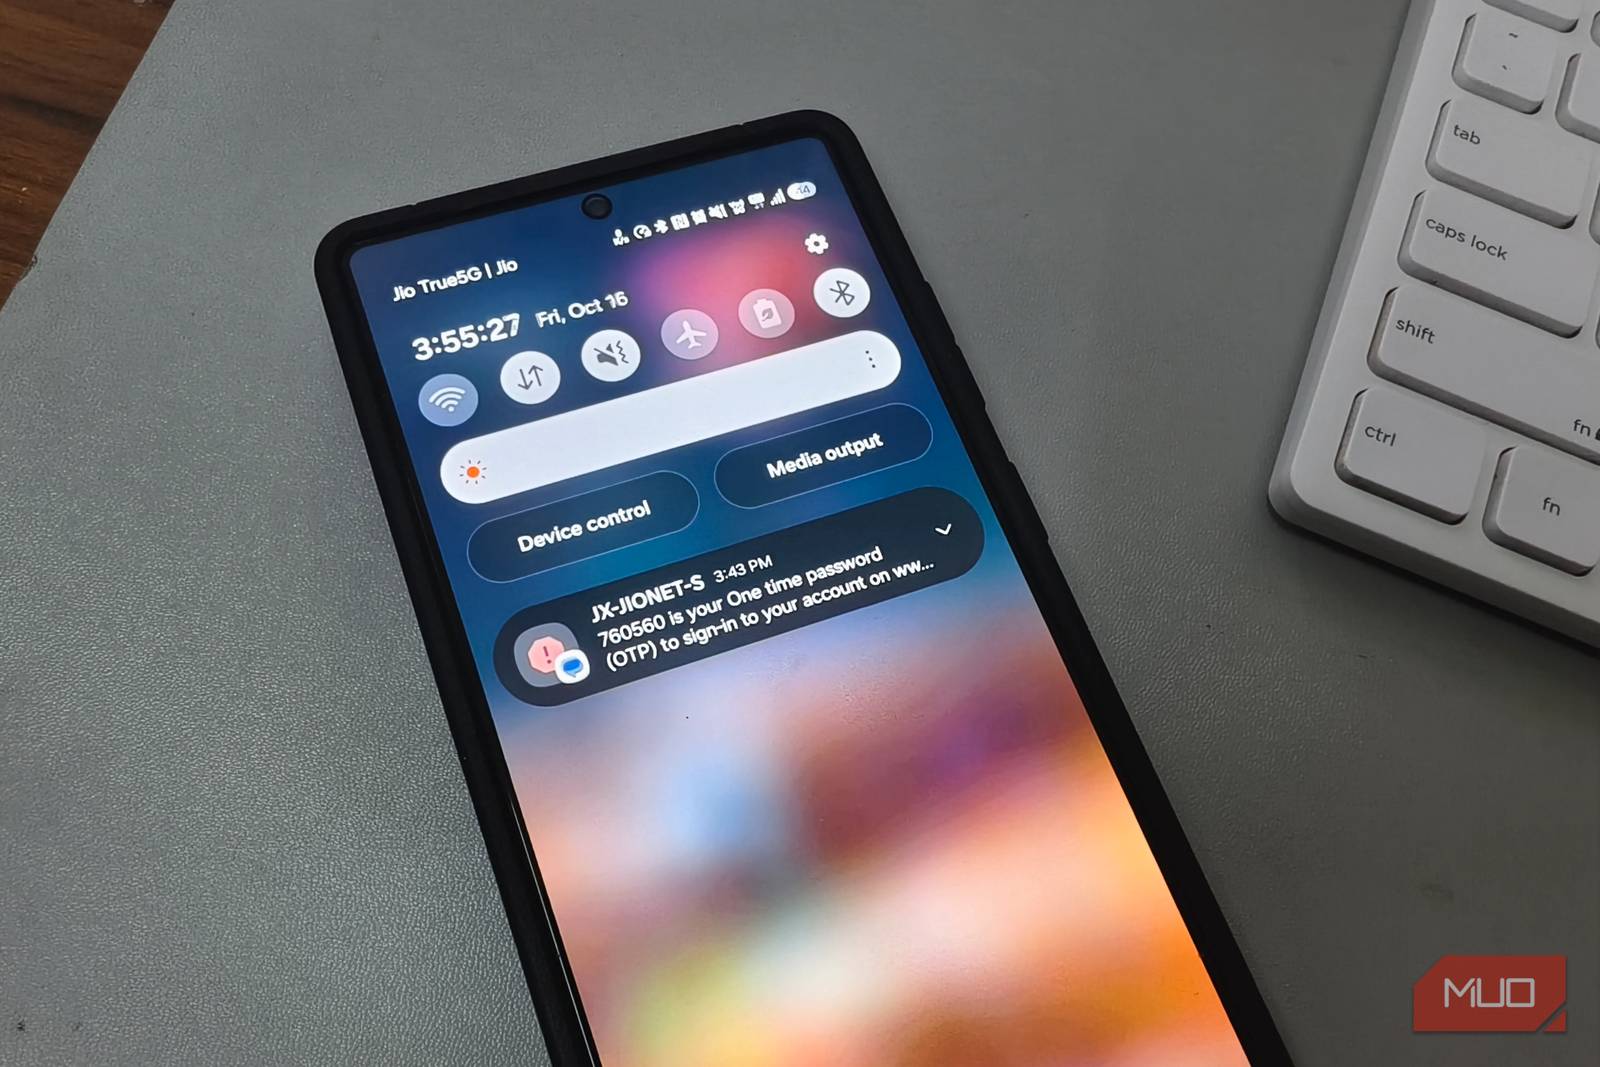

Right now, the most sensitive accounts you own probably depend on a security tool that was never designed to protect you. We give our mobile numbers to banks, password vaults, and email providers, trusting that as long as the phone is in our hand, the account is safe. For years, every time a six-digit code buzzed onto my lock screen, I took it as proof that two-factor authentication was doing its job. Then I started tracing the route that code actually travels after a service sends it, and the path it takes before it ever reaches my phone.
There are several great authenticator solutions, including these five.
When you log in somewhere and a six-digit code arrives by text, that number doesn’t travel through an encrypted channel. Your carrier routes it across Signaling System No. 7, a protocol that telecom networks have used since the early 1980s to handle calls and text messages globally. SS7 was designed when only a handful of state-backed operators touched the network, so the engineers who built it never added authentication. Every command the system receives is treated as legitimate, no questions asked.
That design made sense decades ago, but access to SS7 has spread far beyond those original operators. Smaller carriers, third-party aggregators, and cross-border routing companies all have access now. An attacker with that access can submit a routing request that tricks telecom switches into treating your phone as if it were on a foreign network. Your incoming texts, including any verification codes, quietly reroute to a different device, and your phone never shows a missed message.
This flaw turned real in 2017, when attackers targeted German bank customers on the O2 network. They had already stolen banking credentials through malware on compromised computers, and when the banks sent SMS authorization codes, SS7 commands intercepted them mid-delivery. Account balances were emptied before anyone noticed. Discovering that breach changed my mind about SMS verification, because nothing I do on my end matters when the infrastructure itself treats every operator as trustworthy.
SS7 exploitation demands access to telecom infrastructure, which limits who can pull it off. SIM swapping has no such barrier. In a typical SIM swap scam, someone calls your mobile carrier, pretends to be you, and convinces a representative to transfer your number to a new SIM card. Once the swap goes through, every call and text meant for you lands on the attacker’s device, including every SMS verification code tied to your accounts.
A 2020 Princeton University study revealed just how easy this is. Researchers tested fraudulent SIM swap attempts at five U.S. prepaid carriers and found an 80% success rate. Attackers bypassed security questions by convincing staff to override verification policies. In 2024, T-Mobile and Verizon employees received unsolicited text messages offering $300 for each completed swap.
That kind of access scales fast once the method gets out. In the UK, SIM swap fraud surged 1,055% during 2024, jumping from 289 reported cases to nearly 3,000 in a single year. In Australia, 90% of SIM swap victims had no idea anything had happened until their phone dropped to SOS-only mode. T-Mobile paid $33 million in a private arbitration after a single SIM swap cost a customer over 1,500 Bitcoin. The FCC adopted rules in late 2023 requiring carriers to strengthen their verification, but the wireless industry pushed back and the compliance deadline was waived before it ever took effect.
Switching away from SMS verification turned out to be the easy part. Most services that offer text-based codes also support dedicated authenticator apps. You scan a QR code during setup, and the app stores a secret key locally on your device. From that point, it generates a fresh six-digit code every thirty seconds using nothing but that stored key and your phone’s clock, so the code never leaves your device.
For accounts where the stakes are highest, I added a physical hardware security key. A YubiKey plugs into a USB port or taps against your phone over NFC, and the entire authentication happens through a cryptographic check tied to the specific website domain. A phishing page on a lookalike URL gets no response from the key at all. It costs around $30 for a basic model, and once it’s registered, logging in means plugging in and tapping a button.
I started with email and banking, then worked through cloud storage, social media, and anything else that still had SMS as the default. Every service I switched was one fewer account depending on a text message to keep it safe.
A few simple steps a day keep the hackers and cybercriminals away.
The biggest risk with SMS verification isn’t that better options don’t exist. It’s that the default never asks you to consider them. Carriers, platforms, and login screens still treat a text message like a secure channel, and unless you go looking for the alternative, nothing in the process tells you otherwise.
The YubiKey Security NFC Key is a compact hardware key providing strong two-factor authentication via USB-A or NFC for secure login on computers and mobile devices. It uses phishing-resistant two-factor authentication via FIDO2/U2F. Just plug into a USB-C port or tap on an NFC-enabled device, touch the key, and you’re logged in—no battery, apps, or passwords required.
We want to hear from you. Share your perspective in the comments below, and please keep the conversation respectful.
Your comment has not been saved
This space is open for discussion.
Be the first to share your thoughts.
The best of MakeUseOf, directly in your inbox.
By subscribing, you agree to receive newsletter and marketing emails, and accept our Terms of Use and Privacy Policy. You can unsubscribe anytime.